- 2025-11-18
- Technical
- By Pyxis Communication
Simulate to Survive: How Controlled Cyberattacks Strengthen Real-World Defense
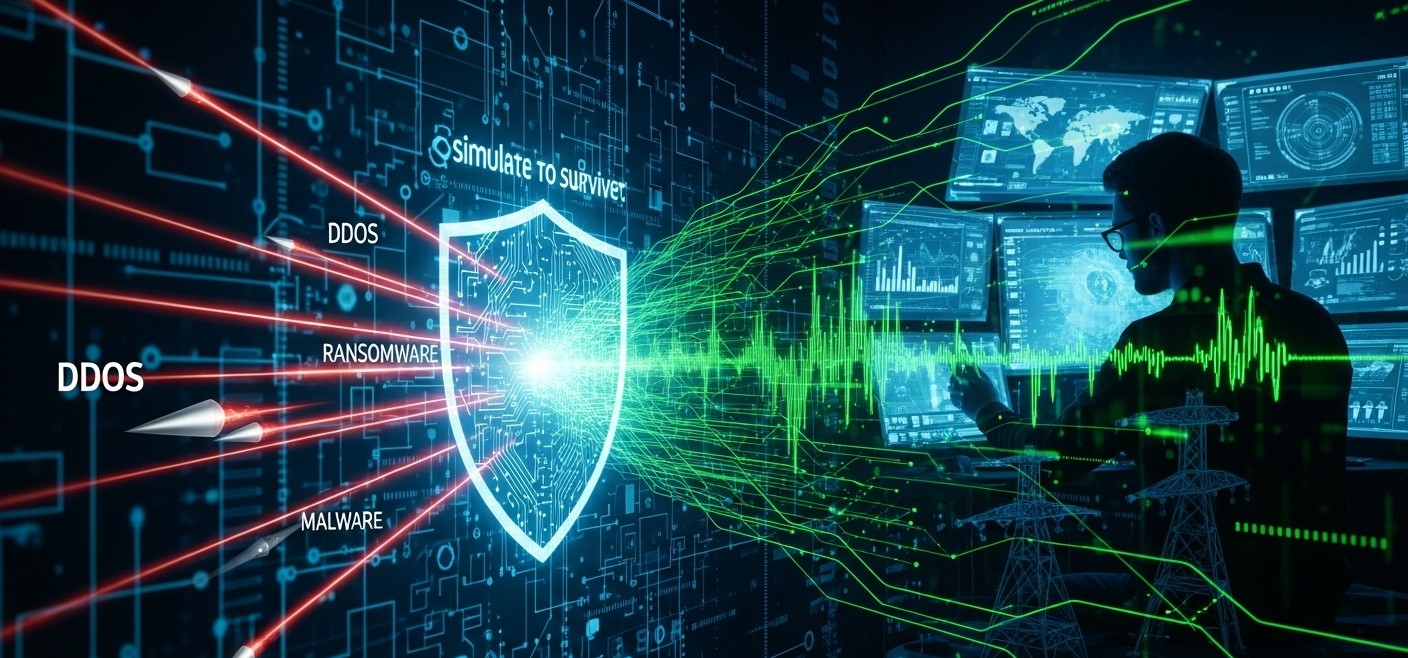
Talk presented by Josmell Chavarri (Information Security Professional at Pyxis) & Edgar Salazar (Offensive Security Tech Lead at Pyxis) – at Open Tech 2025, held on Saturday, September 6, 2025.
Summary
In an increasingly hostile digital landscape, controlled cyberattack simulations allow defensive teams to practice, fail, and improve without putting real systems at risk.
This talk explored—from both offensive and defensive perspectives—how an attack is planned, executed, detected, and responded to, revealing early indicators, critical roles, and key opportunities to strengthen organizational resilience. Pyxis promotes this conversation and supports organizations seeking to mature their defensive capabilities through realistic, simulation-based practices.
The Uncomfortable Truth: Attacks Happen… Whether We Prepare or Not
Cybersecurity carries a truth that’s a little (or very) frightening:
Attackers train every day. Defenders… whenever they can.
That asymmetry explains why so many incidents manage to slip into corporate environments. Not always because of missing tools, but because of a much more human problem: lack of practice.
With that premise—and a good dose of their trademark humor—Josmell Chavarri and Edgar Salazar opened their talk at Open Tech 2025. Their message was clear:
“We don’t need to wait for a real attack to learn. We can simulate it. We can make mistakes without losing anything. We can rehearse before it hurts.”
And that kicked off a journey that blended offensive pedagogy, defensive insight, battlefield anecdotes, and a live technical demonstration that left the audience thinking, “Wow… this happens way more often than I thought.”
Why Simulating Attacks Matters (A Lot)
Today’s digital ecosystem is a silent jungle.
It makes no noise… until it does.
Threats multiply, automate, and professionalize:
- Ransomware-as-a-service
- Organized criminal groups
- Illicit cryptomining
- Mass exploitation of newly published vulnerabilities
- AI-enhanced social engineering
And the list grows every month.
Meanwhile, organizations do their best—installing patches, checking logs, responding to alerts—until an incident exposes a hard truth:
Theory isn’t enough. In security, whoever doesn’t train… loses.
That’s why attack simulation becomes a strategic tool. It allows teams to:
- practice early detection
- validate response processes
- adjust roles
- identify blind spots
- and most importantly, gain flight hours
As Edgar put it:
“We can have the best firewall on the planet… and still, the first real incident will catch us with wires crossed if no one knows what to do.”
Two Perspectives, One Goal:
Attack to Learn, Defend to Survive**
One of the strongest components of the talk was the interplay between the offensive (Red Team) and defensive (Blue Team) perspectives.
Far from being separate worlds, they were presented as two complementary sides of the same coin.
The Offense: Thinking Like an Attacker
Josmell began by explaining how a modern attack is structured. No Hollywood theatrics—the real thing is far more methodical.
An attacker typically:
- Performs reconnaissance
- Exploits a vulnerability
- Gains access
- Moves laterally
- Establishes persistence
- Exfiltrates data or executes damaging actions
All following well-known frameworks like the Cyber Kill Chain or the MITRE ATT&CK matrix.
And the key insight:
This knowledge isn’t “just for hackers.”
Understanding it is essential for any defensive team that wants to anticipate threats.
As Josmell joked:
“If you want to defend your house, at least know where the thieves come in.”
The Defense: Reading Logs Like Your Life Depends On It
From the defensive trenches, Edgar explained how an attack—any attack—leaves traces.
Even skilled attackers make noise.
Problems arise when no one is looking, correlating, or understanding what they’re seeing.
Suspicious signs include:
- Creation of unexpected files
- A process running as root without justification
- A new binary inside /tmp
- A suspicious change in permissions
Small signals… but enough to prevent a disaster if detected early.
Defense, Edgar said, is a game of being “semi-paranoid without fully collapsing.”
Attackers’ Hall of Fame: Akira, Kinsing & Other Chaos Specialists
A highlight of the talk was the overview of real criminal groups currently affecting organizations worldwide.
Akira
- Ransomware and double extortion specialists
- Fast, methodical, persistent
- Turn small mistakes into major breaches
Kinsing
- Masters of illicit cryptomining
- Infect Linux servers and container environments
- Convert corporate resources into mining farms
What do these groups have in common?
- Aggressive automation
- Sophisticated lateral movement
- Clever persistence
- Fast exploitation of freshly disclosed vulnerabilities
- Long-running campaigns
As Josmell put it:
“They’re not geniuses. They’re efficient. And if we don’t train, they win by walkover.”
The Magic Happens at the Edge:
Where Offense and Defense Work Together**
This is where the Purple Team comes into play.
Not a mythical “hybrid expert,” but a collaborative practice where offensive and defensive teams work side by side.
They described it simply:
- Offense teaches how attackers think
- Defense explains what can actually be detected
- Together they find gaps, adjust controls, and harden processes
Edgar summed it up beautifully:
“We don’t need a unicorn that does everything.
We need teams that speak the same language.”
The Demonstration: When a Simulated Attack Comes Alive
The room was calm.
Until Caldera, the simulation tool, took the stage.
In just a few minutes:
- Files appeared as if by magic
- Others vanished
- Processes ran where they shouldn’t
- Suspicious activity popped up in /tmp
- Commands executed with elevated privileges
All signals that—when correlated—told the story of a full attack.
Meanwhile, Wazuh lit up with alerts that, when interpreted correctly, allowed immediate response.
More than one person in the audience wondered:
“How many times has something like this happened in my infrastructure… and no one noticed?”
The Key Lesson: Practice Builds Resilience
By this point, the conclusion was inevitable:
You can’t defend what you never train.
Simulations allow teams to:
- Fail without real consequences
- Learn in a safe environment
- Test incident-response playbooks
- Adjust internal processes
- Improve cross-team coordination
- Build a shared technical language
They are a gym for defensive teams.
Or, in Josmell’s words:
“Attackers practice daily. We should at least practice a little.”
The Future: Faster Attacks, Smarter Defenses
In the coming years, attacks will become:
- more automated
- more AI-assisted
- harder to detect
- more extortion-oriented
- faster at exploiting new vulnerabilities
And yet the talk closed on a hopeful message:
Defenses can evolve too.
With the right tools, collaboration, ongoing simulations, and strategic focus, organizations can become significantly more resilient.
The talk ended with a phrase that captured the spirit of the day:
Simulating isn’t playing. Simulating is preparing. And preparing is the best defense we have.
Tags
adversary emulationAkira ransomwareBlue TeamCalderacryptomining attackscyber attack simulationCyber DefenseCyber Kill Chaincyber resiliencecyberattackscybersecurityCybersecurity Trainingdefensive securityIncident ResponseKinsing malwareMITRE ATT&CKoffensive securityOpen Tech 2025organizational resiliencepurple teamPyxisransomwareRed Teamsecurity operationssimulated attacksSOCthreat detectionThreat HuntingWazuh
With a 360° potential, our solutions matrix accompanies the lifecycle of any project, with skills and experience in Development, Design, Q&A, Devops, Operation & Deploy, and Architecture
Discover all post